Why it is not just Salt
18 things free Salt tools do not do
Open-source Salt is a strong engine. Five of the things Gardience adds are shown running in the real deployment below; the rest of the list follows.
1 Directory sign-on + role-based access
# an operator logs in through the directory and runs the fleet
$ login alice  ·  run test.ping '*'
  {'win-mock-01': True, 'linux-web-01': True, 'linux-db-01': True}

# a viewer is allowed to look, but blocked from a privileged action
$ login bob    ·  run pkg.install nginx '*'
  HTTP 401 Unauthorized  (denied by role)

# a wrong password never gets in
$ login alice  ·  password WRONG
  HTTP 401 Unauthorized
→Real single sign-on against Active Directory or LDAP, with roles that actually stop the wrong person. Plain Salt signs in through its own auth, with permissions hand-written in the master's config.
2 Tamper-evident audit log
$ verify audit chain
  {'entries': 39, 'chain_intact': True}

# change a single byte of the log and verify again
$ tamper one record  ·  verify audit chain
  {'entries': 39, 'chain_intact': False}
→Every action is hash-chained. If anyone edits the record, verification fails. That is what an auditor wants to see.
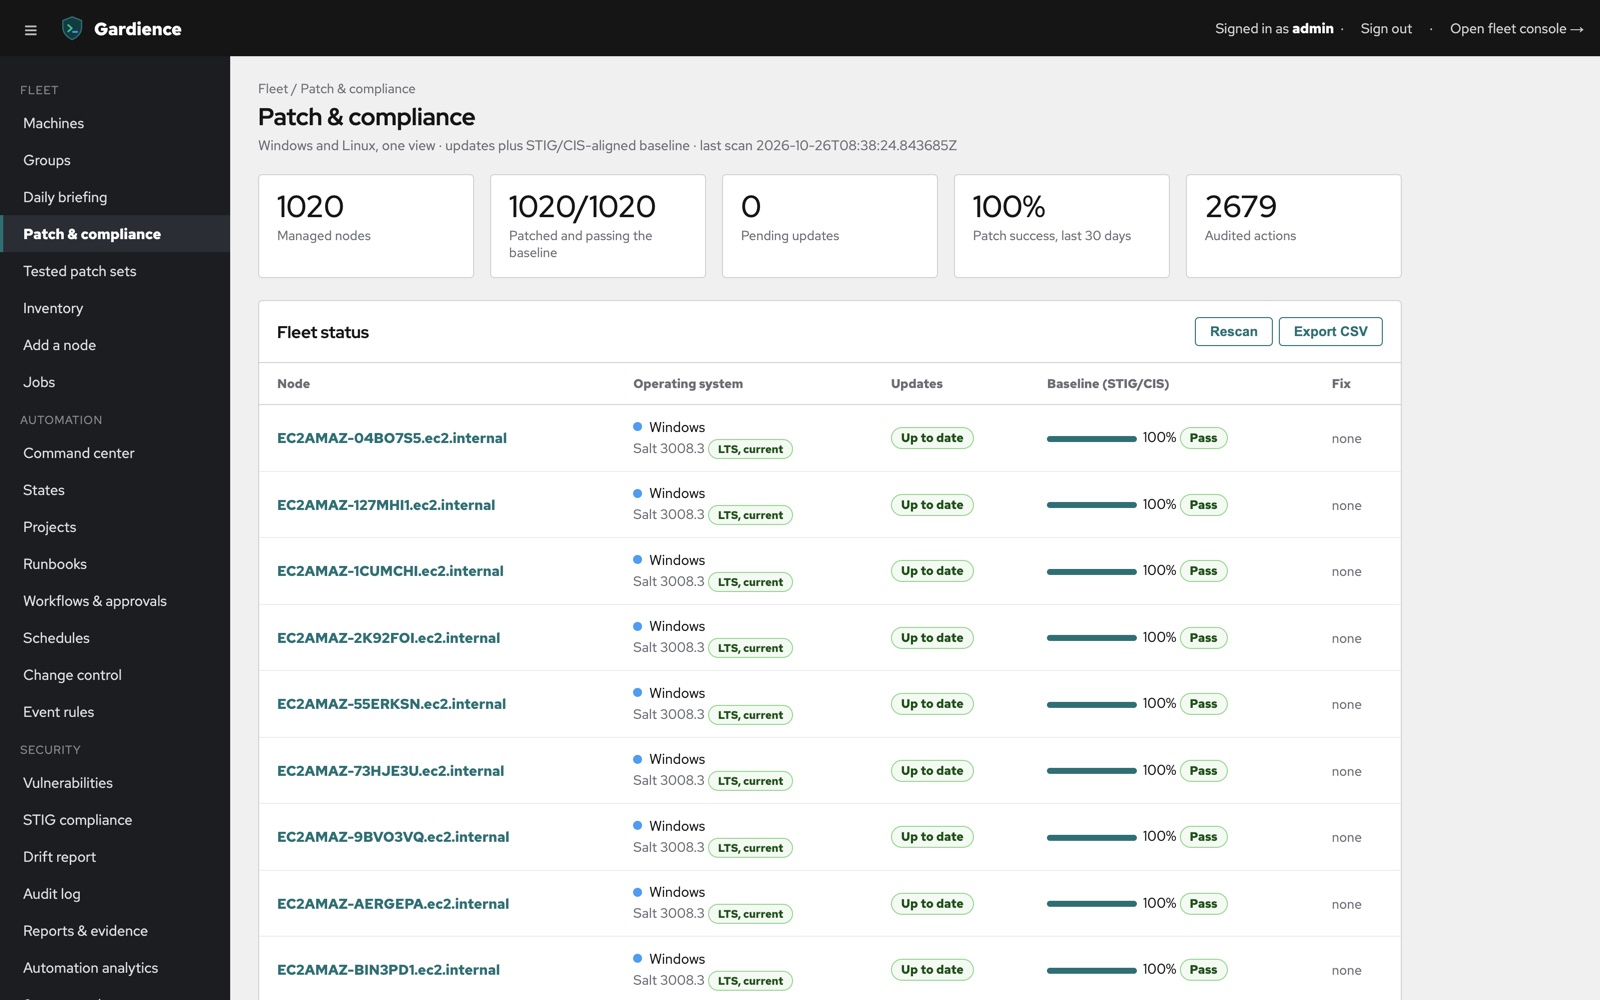
3 Patch & compliance across both OSes
$ scan fleet
  win-mock-01   Windows  pending=3   compliant=False   KB5034441, KB5034765, KB890830
  linux-db-01   Debian   pending=1   compliant=False   liblzma5
  linux-web-01  Debian   pending=1   compliant=False   liblzma5
  exported: compliance.csv
→Windows Update status and Linux package status in one report, exportable for an audit. One tool, not two silos.
4 Tested, pinned releases
$ release smoke-test
  PASS  HTTP :80 redirects to HTTPS
  PASS  directory login issued a token
  PASS  wrong password rejected (401)
  PASS  operator reached the whole fleet
  PASS  RBAC denied the viewer (401)
  PASS  compliance reports Windows and Linux
  PASS  audit log intact
  RESULT: 7 passed, 0 failed  :  RELEASE OK
→Every release runs this gate before it ships, so a Salt upgrade never silently breaks your console.
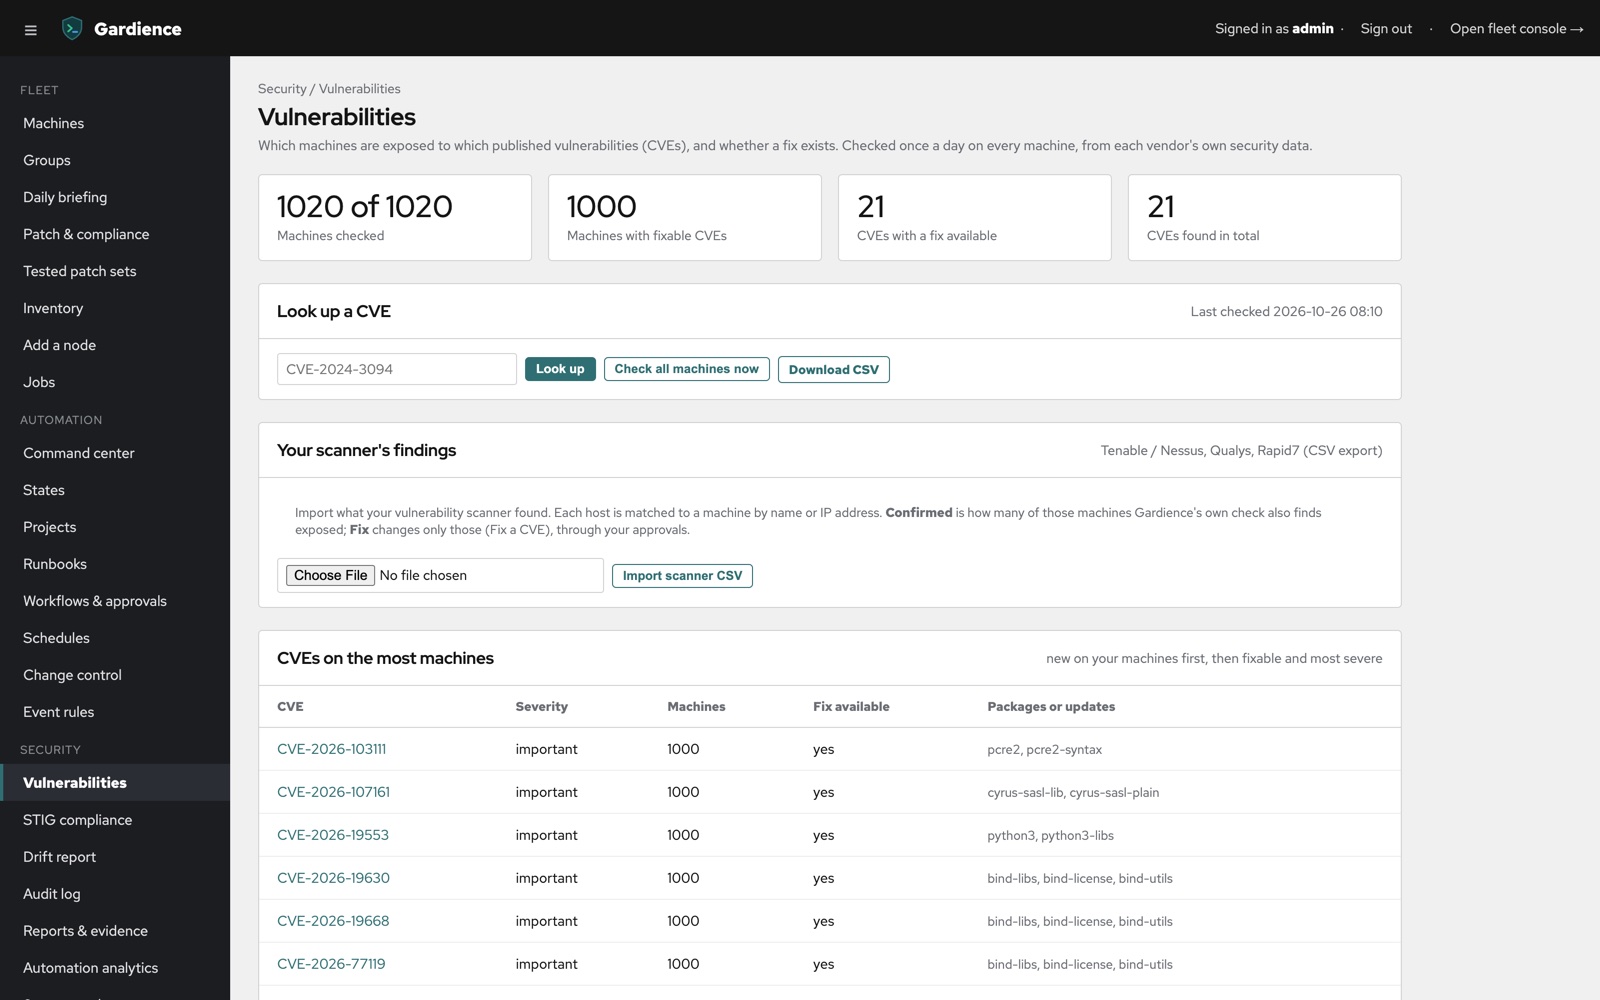
5 CVE watch behind the SLA
$ cve-watch  (previous release: salt==3006.9, tornado==6.4.1)
  advisories affecting the bundle: 48
   - salt 3006.9: CVE-2025-22236  minion event bus auth bypass
   - salt 3006.9: CVE-2025-22237  pillar command injection
   ... 46 more

$ cve-watch  (current release: salt==3008.3, tornado==6.5.10)
  advisories affecting the bundle: 0
  upgrade tested on Windows and Linux, shipped
→We watch the exact versions you run and ship a fix inside the SLA. Our own move to Salt 3008 took the bundle from 48 known advisories to zero, tested on real Windows and Linux before it shipped.
And the rest of the list
- GuardrailsTwo-person approval, change windows, machine locks, and break-glass access.
- Security baselineA STIG/CIS-aligned baseline scored on every machine, with one-click fixes and drift repair.
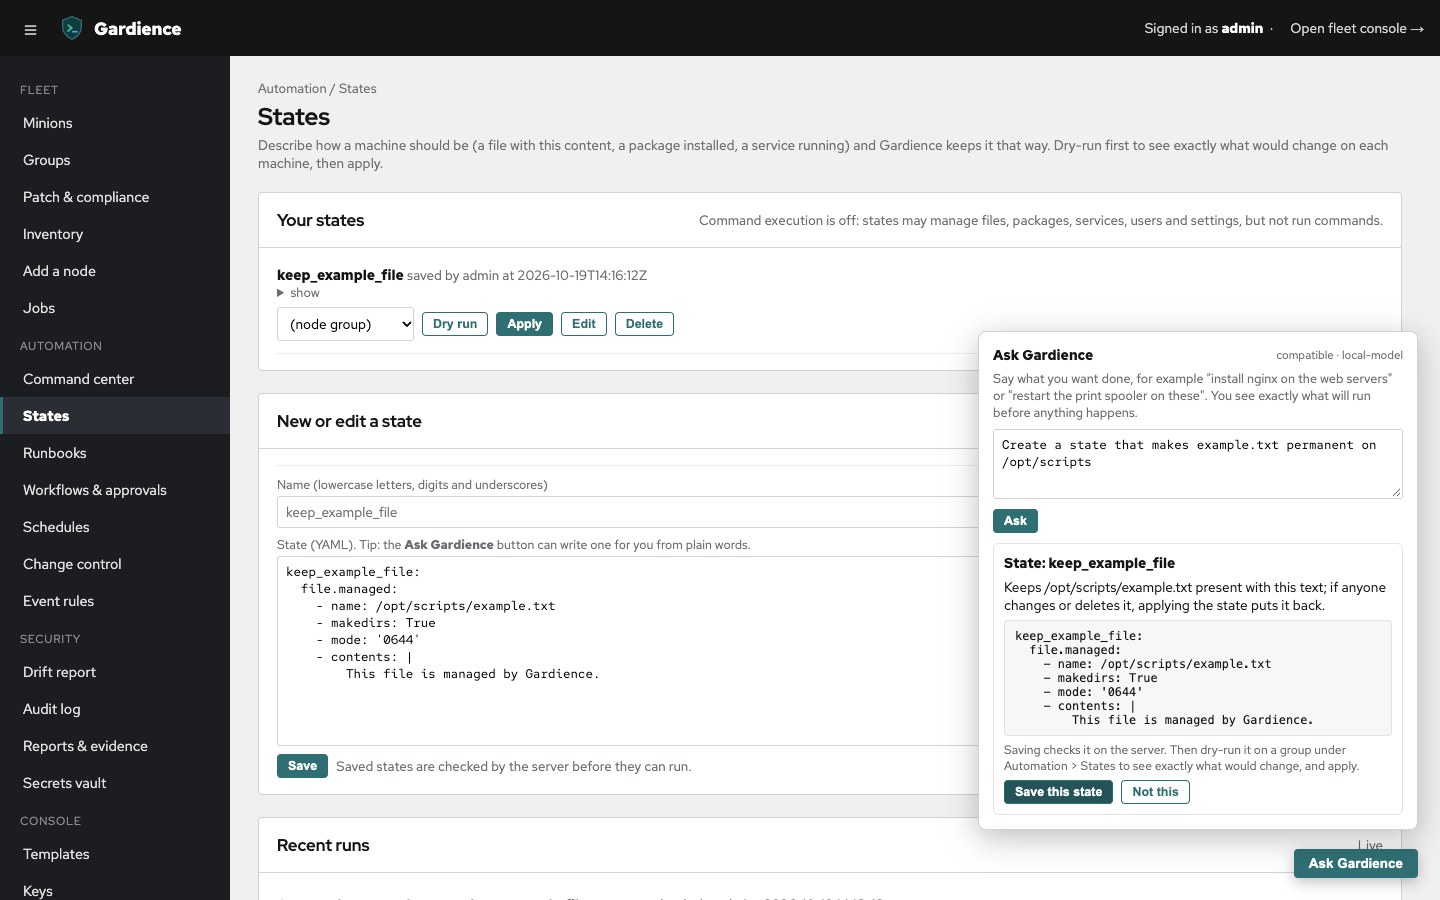
- AI assistantWrites the exact Salt command or state from one sentence, and runs nothing until a person approves it.
- Command centerForms and plain-words search, so people who do not know Salt syntax can run the common tasks.
- Ansible playbooksYour existing playbooks run over the Salt connection, on Windows too, with no WinRM.
- Self-healingEvent rules restart a stopped service within seconds, warn about a filling disk, and configure each new machine on first boot.
- Patch ringsPending updates per machine, a pilot ring before the broad one, and reboots handled in the window.
- Evidence packA signed export of fleet status, baseline results, change results, and the audit log for an assessor.
- TerraformA published provider, so machines you build join on first boot, get their state, and leave the fleet when destroyed.
- API and MCPA REST API with scoped keys, and an MCP server so Claude, Cursor, or Copilot can answer questions about the fleet.
- High availabilityA warm standby server with fencing, and site proxies so a remote network needs one firewall opening.
- Install and offlineOne command to install, and a fully offline install for air-gapped networks.
- SupportSomeone accountable when it breaks, tested releases, and a CVE-fix SLA.