CMMC Level 2 and STIG, built in.

From an SPRS score of −203 to 110: Gardience handled the technical side in 35 minutes. Hardening you can show an assessor, a fully offline install, and evidence an assessor can check, from a SAM-registered company.

Evaluating Gardience for CMMC or a government fleet? Pick the easy way.

No sales cycle, no forms to fill in. Choose one:

See it in 15 minutes

Pick a time. We walk through a live Windows and Linux fleet, your questions first.

Pick a time

Get a pilot plan

Your work email is all we need. Within one business day: a pilot plan for your fleet, answers to the security questions your team will ask, and pricing.

Try it yourself

Free for 90 days on up to 25 machines, no credit card. Installs in 4 to 5 minutes on one Linux server.

Start free trial
CMMC Level 2 for defense contractors

From −203 to 110. Gardience handled the technical side in 35 minutes.

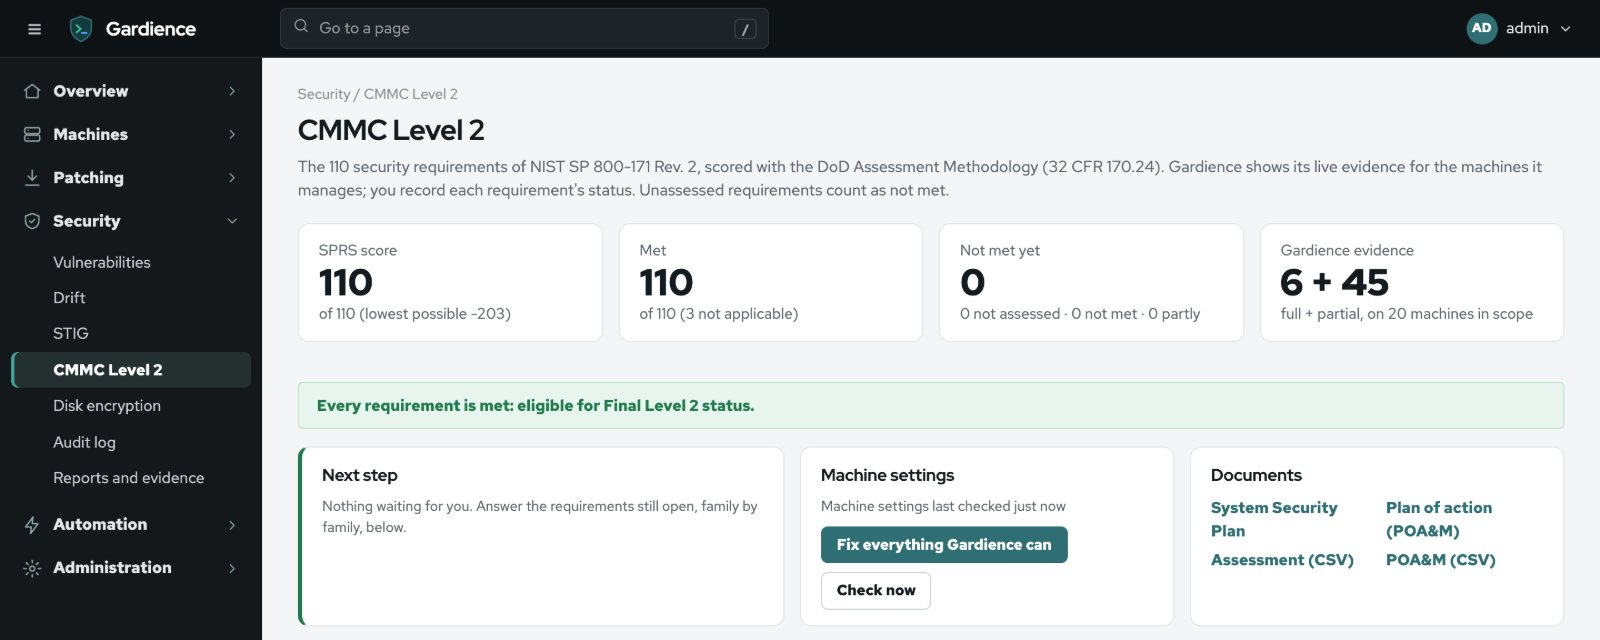
On a 50-machine test network, Gardience patched, hardened, and BitLocker-encrypted all 20 Windows servers that hold controlled data, set every CMMC setting, and wrote the statements for every requirement the machines can prove. It gives you 14 policy templates and a checklist of the proof assessors ask for. You fit the policies to how your company works and upload your proof, and the score updates as you go.
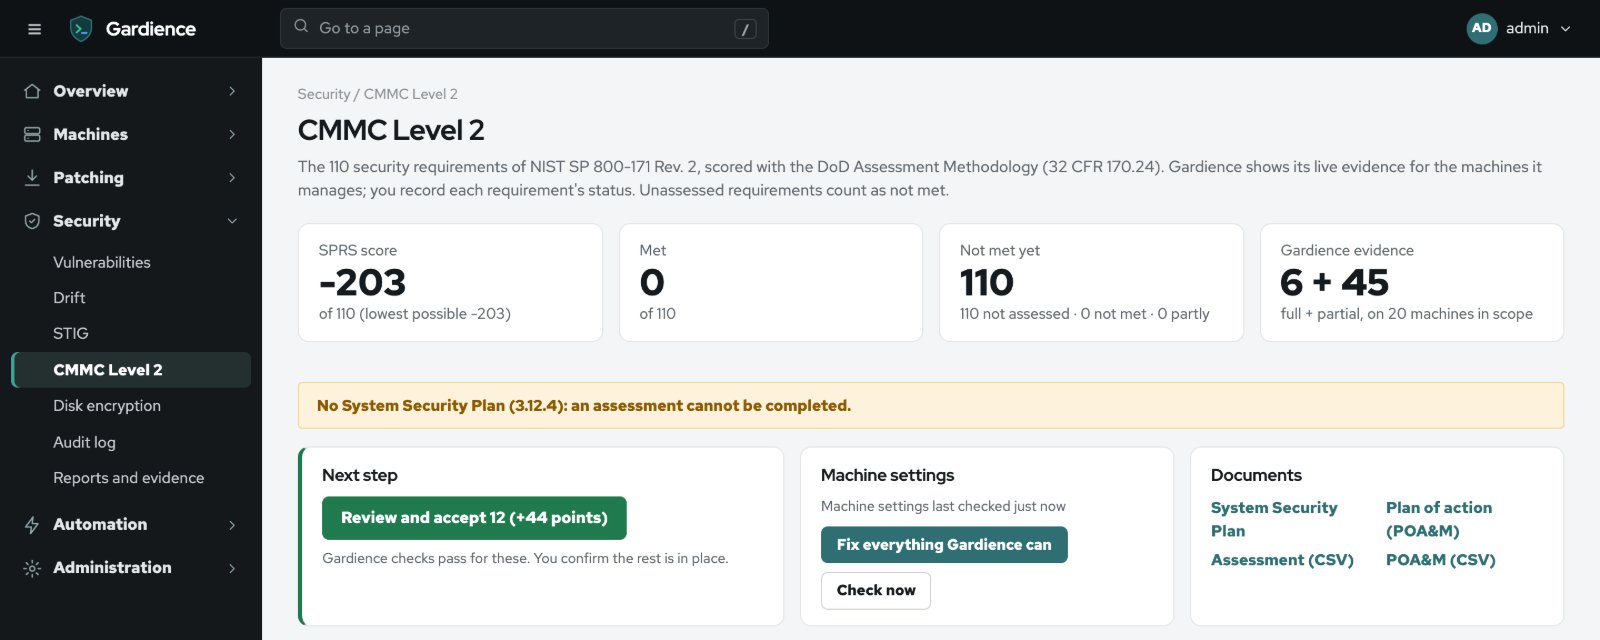
CMMC Level 2 before: SPRS score -203, no requirements met
Before: nothing recorded, machines unpatched and unencrypted. SPRS −203.
CMMC Level 2 after: SPRS score 110, every requirement met
After: servers fixed in 35 minutes, policies and proof uploaded. SPRS 110, every requirement met.

All 110 requirements

Every NIST SP 800-171 requirement tracked with its status, its evidence, and a live SPRS score.

Machines prove about half

Machine checks on Windows and Linux cover 51 of the 110 requirements, and most failing settings are fixed in one click. Okta, Microsoft 365, and a termination report from your HR or payroll system add evidence for sign-ins and people who left.

Review and accept

Statements drafted for every requirement the checks prove. Accept them in one step, or let the score follow the evidence as it changes.

Ready for your assessor

System Security Plan, plan of action (POA&M), and a signed evidence pack, all from the same data.

Alerts when something slips

A requirement marked Met whose check starts failing is flagged right away, so the score you report stays true.

BitLocker without lost keys

Drives are encrypted only after each recovery key is in the vault and in a kit kept off the server.

Small contractors spend $70,000 to $250,000 getting ready. Gardience is $10,000 a year.

Much of that bill is consultants at $250 to $400 an hour doing the work Gardience automates: patching, hardening, encryption, CMMC settings, and the statements that prove them. Starter is $6,000 a year and CMMC Level 2 adds $4,000, both included in the free 90-day trial. The assessor’s fee is separate either way.

Ranges are published industry estimates of first-year cost; the DoD’s own estimate for the Level 2 assessment alone is about $105,000 over three years.

Where CMMC stands today

The DoD paused Phase 2, the third-party assessments, on July 13, 2026. Phase 1 stays in force: Level 1 and Level 2 self-assessments, and the SPRS score you report, are still required in contracts. What still applies
DISA STIG

STIG scans, STIG Viewer checklists, and an eMASS POA&M from one console.

Gardience scans your Linux servers against DISA’s STIG every week, shows each machine’s CAT I, II, and III findings, and writes the paperwork for you: a STIG Viewer checklist for every machine and a POA&M in eMASS’s import layout. Nothing to buy from DISA, and nothing to download by hand.

Weekly DISA STIG scans

OpenSCAP with the DISA STIG profile on RHEL, Rocky Linux, AlmaLinux, Oracle Linux, CentOS Stream, and Ubuntu 22.04 and 24.04. Machines with CAT I findings come first. Scans change nothing on the machine.

Checklists for STIG Viewer and eMASS

One .ckl per machine, built from DISA’s own STIG file with DISA’s rule numbers, check text, and CCIs. Passed is Not a Finding, failed is Open, and anything a person must check is left Not Reviewed for you.

POA&M in eMASS’s layout

Every open STIG finding under its NIST SP 800-53 control, plus every CVE Gardience finds, with DISA’s fix text and due dates by severity. Exploited CVEs get CISA’s due date.

DISA’s files, fetched for you

Gardience downloads the STIGs your machines need from DISA and checks weekly for a newer release. On a network without internet, add the STIG zip yourself in one step.

Windows hardened too

Windows servers get a scored STIG- and CIS-aligned baseline with one-click fixes and drift repair, patching, BitLocker, and CVE checks, all in the same console and the same evidence pack.

Every download on the record

Every scan, checklist, and POA&M download is in the tamper-evident audit log, and people limited to some machines see only those machines.

Results show how machines measure against the STIG’s automated checks; your assessor still reviews the checklist. Windows .ckl checklists are not produced, because DISA’s Windows checks run only in DISA’s SCAP Compliance Checker. How STIG works in Gardience · STIG and CIS evidence an assessor accepts

For government and regulated shops

Built to sit inside a STIG or CMMC boundary, from a SAM-registered company with cleared people.

DoD and regulated environments run Windows everywhere and answer for every endpoint. Gardience gives them one supported console for the whole fleet, hardened by default and provable to an assessor, with a U.S. company standing behind it and a CVE fix SLA.

Hardening you can show

A scored STIG/CIS-aligned baseline on every Windows and Linux machine, one-click remediation, drift detection and repair, and a NIST SP 800-53 control mapping in the docs.

Air-gapped by design

Installs from a signed offline bundle with every image prebuilt, patches Windows from offline update bundles, and Linux from your mirror, and phones home to no one. The AI assistant can run on a model inside your enclave.

Evidence an assessor can check

A tamper-evident audit log of every action and every machine's result, forwarded to your SIEM, and a signed evidence pack an assessor checks offline with our verifier. For the proof only people can give, Gardience sends each person one link to upload their records and sign the policies, and reminds them until it is done.

Least privilege, enforced

Single sign-on or Active Directory with one-time codes and roles, two-person approval, change windows, and machine locks. Arbitrary commands are off by default, enforced by Salt itself, and break-glass access is time-limited and audited.

Supply chain you can verify

Every release is signed, ships an SBOM for every image, and is cut only after a full release check: a simulated 10,000-machine scale test, OWASP ZAP, nuclei, TLS scans, and published Salt exploit tests.

Stays up

A warm standby with automatic failover, site proxies for remote enclaves, and 1,020 Windows and Linux servers patched in 13 minutes in one two-person-approved run, every machine's result in the audit log and a signed evidence pack.

Bouziden Management LLC is registered in SAM (UEI Y5LBHH9WJ399, CAGE 22VQ0) under NAICS 541512 and qualifies for small-business set-aside contracts. Government pays the same prices as everyone else: an office with 100 machines buys Starter at $6,000 a year, by card or purchase order (pricing). Capability statement · NIST 800-53 mapping · Security details

Already running Uyuni, SUSE Manager, or Broadcom's Salt console?

That is the easiest fit. Keep your states, pillars, and agents. Gardience takes the Windows half or the whole fleet, and Broadcom shops move off the 2028 end of support at a flat price.
Ready to try it? Free for 90 days on up to 25 machines, no credit card. Installs in 4 to 5 minutes.
Get in touch

Tell us about your fleet.

Two or three lines is enough. A person will reply and set up a short call to size it.

Evaluating Gardience?Three easy ways:15-minute walkthroughPilot plan by emailStart free